
Kubernetes Security Checklist 10 Steps to Follow

Aziro Marketing
2025-06-25
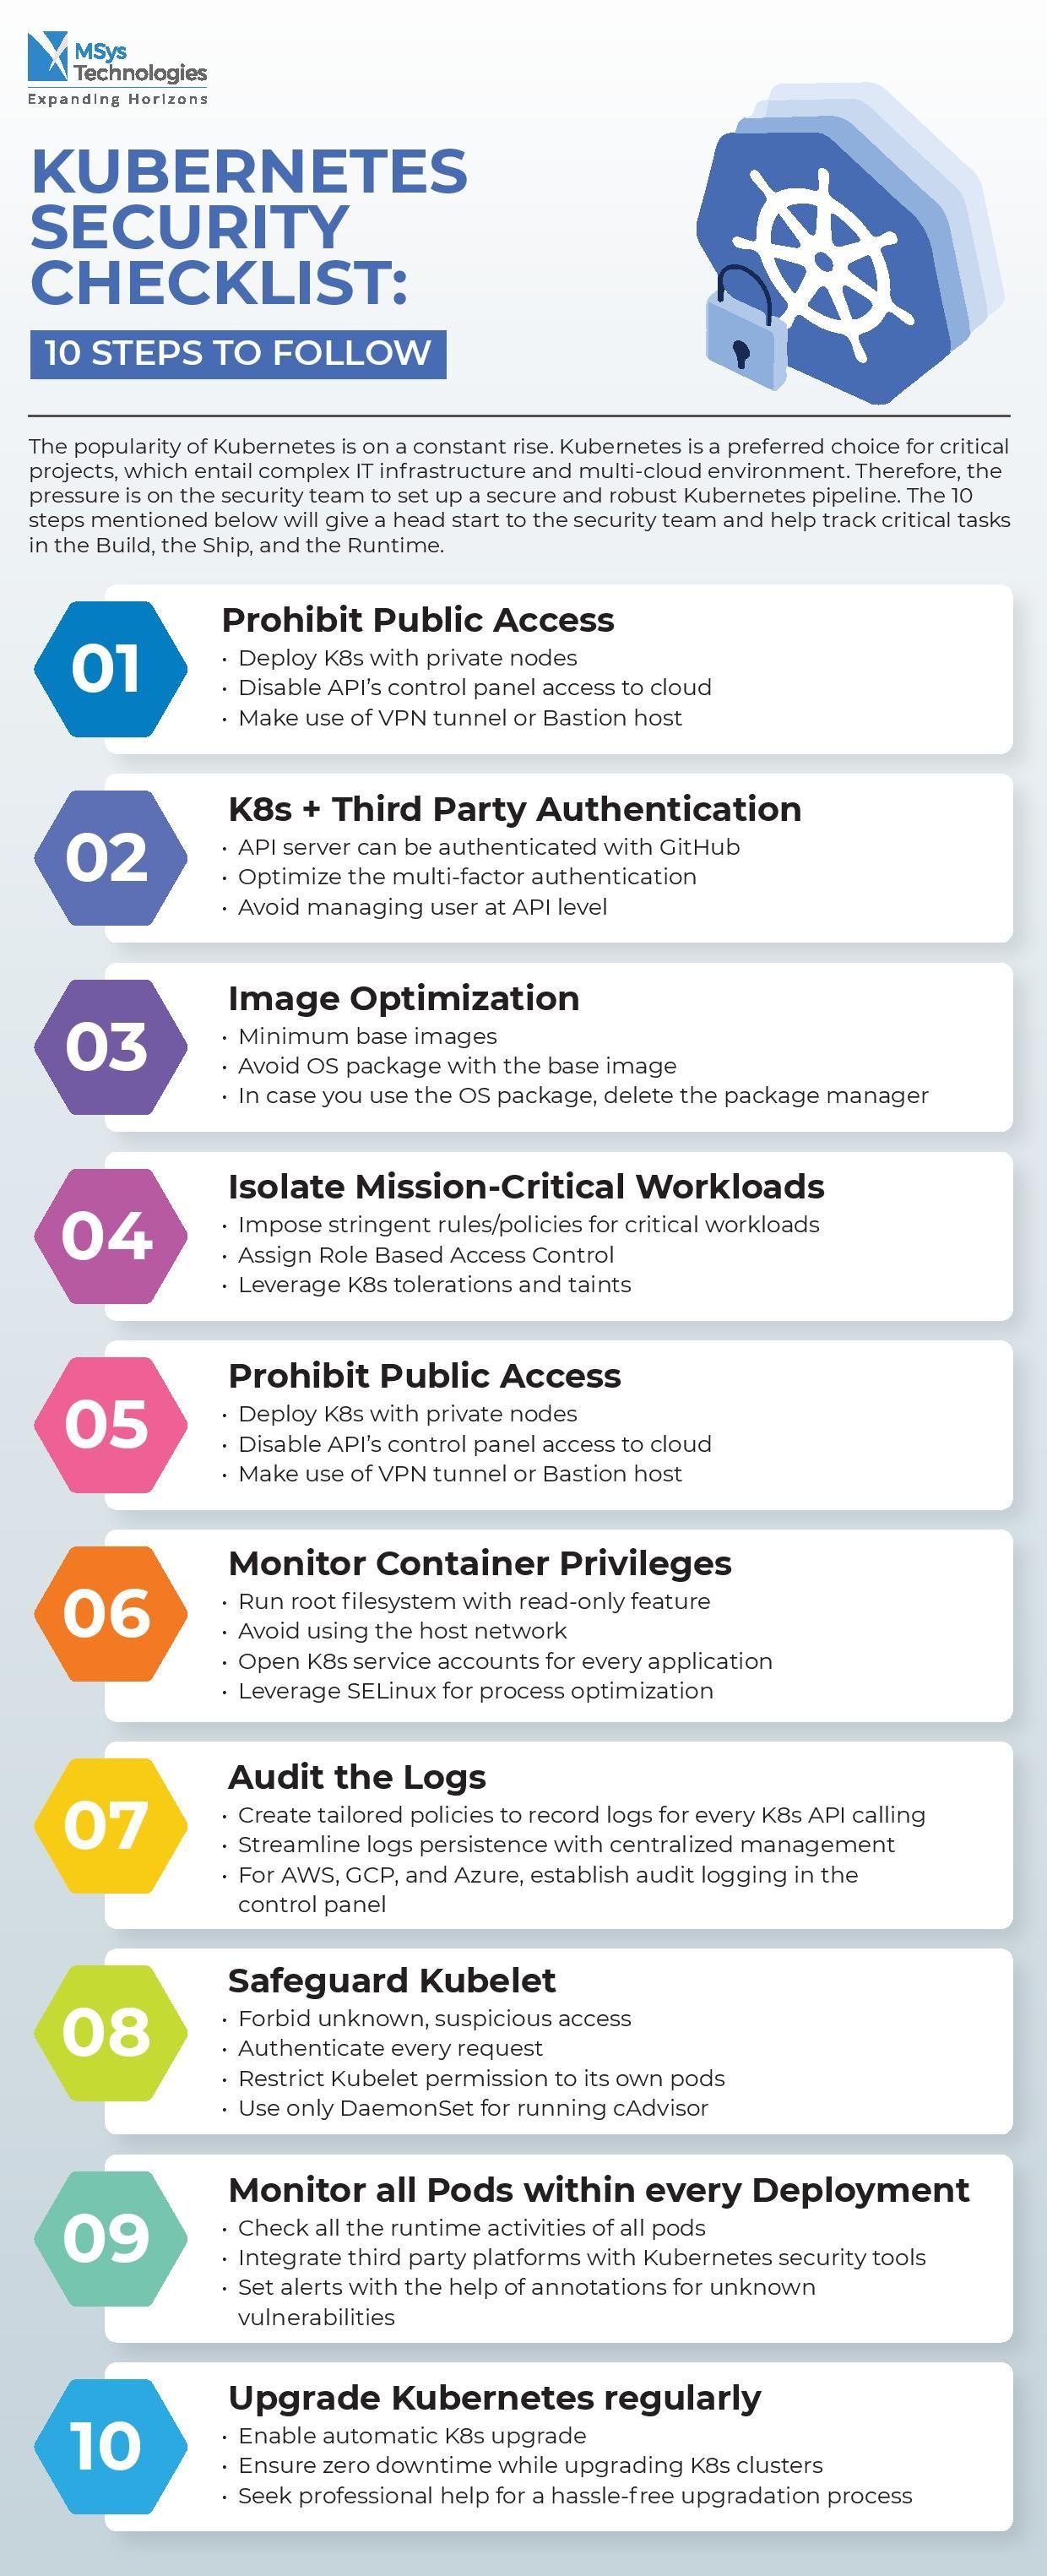
A strong Kubernetes security checklist starts with configuring role-based access control (RBAC) to manage user permissions. Ensure network policies are defined to control traffic flow between pods. Use pod security policies to enforce security standards on containerized workloads. Enable audit logging for traceability and monitoring. Regularly scan container images for vulnerabilities before deployment. Implement secrets management to securely handle sensitive data. Ensure strong encryption for data in transit and at rest. Keep Kubernetes components up-to-date to avoid known vulnerabilities. Enforce least privilege access across clusters and environments. Finally, ensure continuous monitoring and alerting to detect suspicious activity. With Aziro’s expertise, these practices ensure a robust and secure Kubernetes environment for your
Partner with our expert AI engineers to turn complex challenges into intelligent, scalable solutions. We blend innovation with precision to build what matters most—future-ready results.. Feel free to contact our team for seamless implementation of next gen solutions.
Real People, Real Replies.
That's how it usually goes, you reach out with a question or a rough idea, a real person at Aziro responds, and a conversation turns into something big.
Start yours with us.

Talk to us
+1 227 232 3176

Drop us a line at
info@aziro.com